Featured Check out our Deep & Dark Web Monitoring Platform — DarkWiser Meet DarkWiser — Dark Web Monitoring

Research & insights

Blog & Research

Original security research, hands-on case studies, and practical guides from the Laburity team.

Research Case Study: Supply Chain Security at Scale – Insights into NPM Account Takeovers

Software supply chains are complex ecosystems where even a single vulnerability can lead to widely spread security issues. This blog focuses on supply chain account takeovers…

Read article

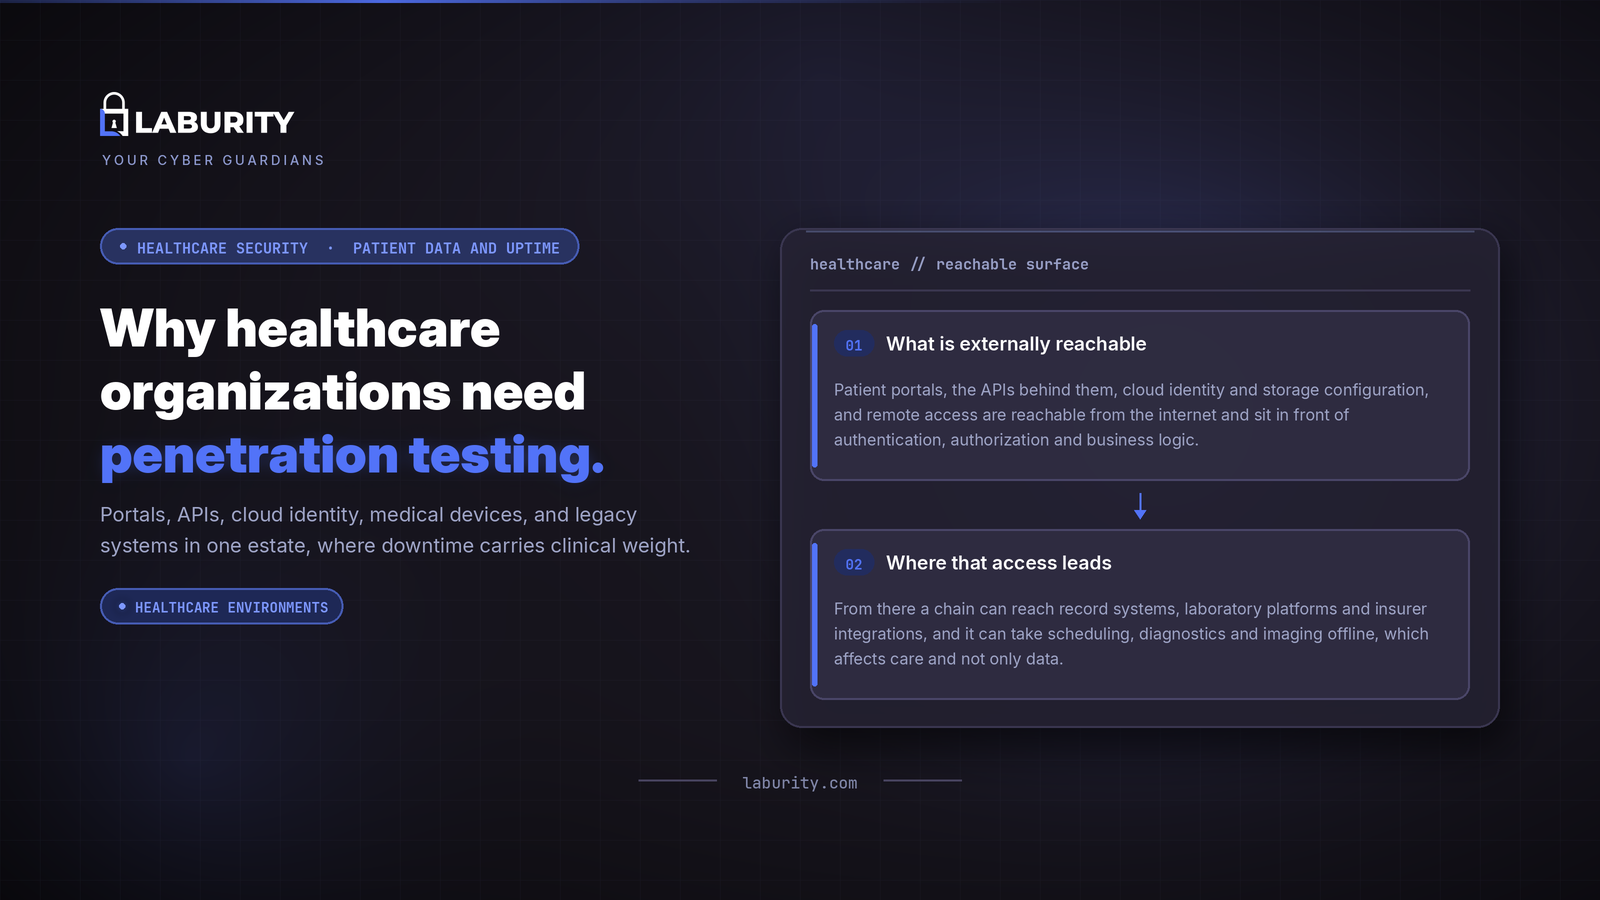
Why Healthcare Organizations Need Penetration Testing

healthcare penetration testing, HIPAA penetration testing, healthcare cybersecurity, patient data security, hospital penetration testing, healthcare API security testing, ePHI security, HIPAA Security Rule update, healthcare vulnerability assessment, medical device security testing, healthcare ransomware risk, electronic health record security, patient portal security testing, healthcare cloud security assessment, broken object level authorization, healthcare network segmentation, legacy system

Read article

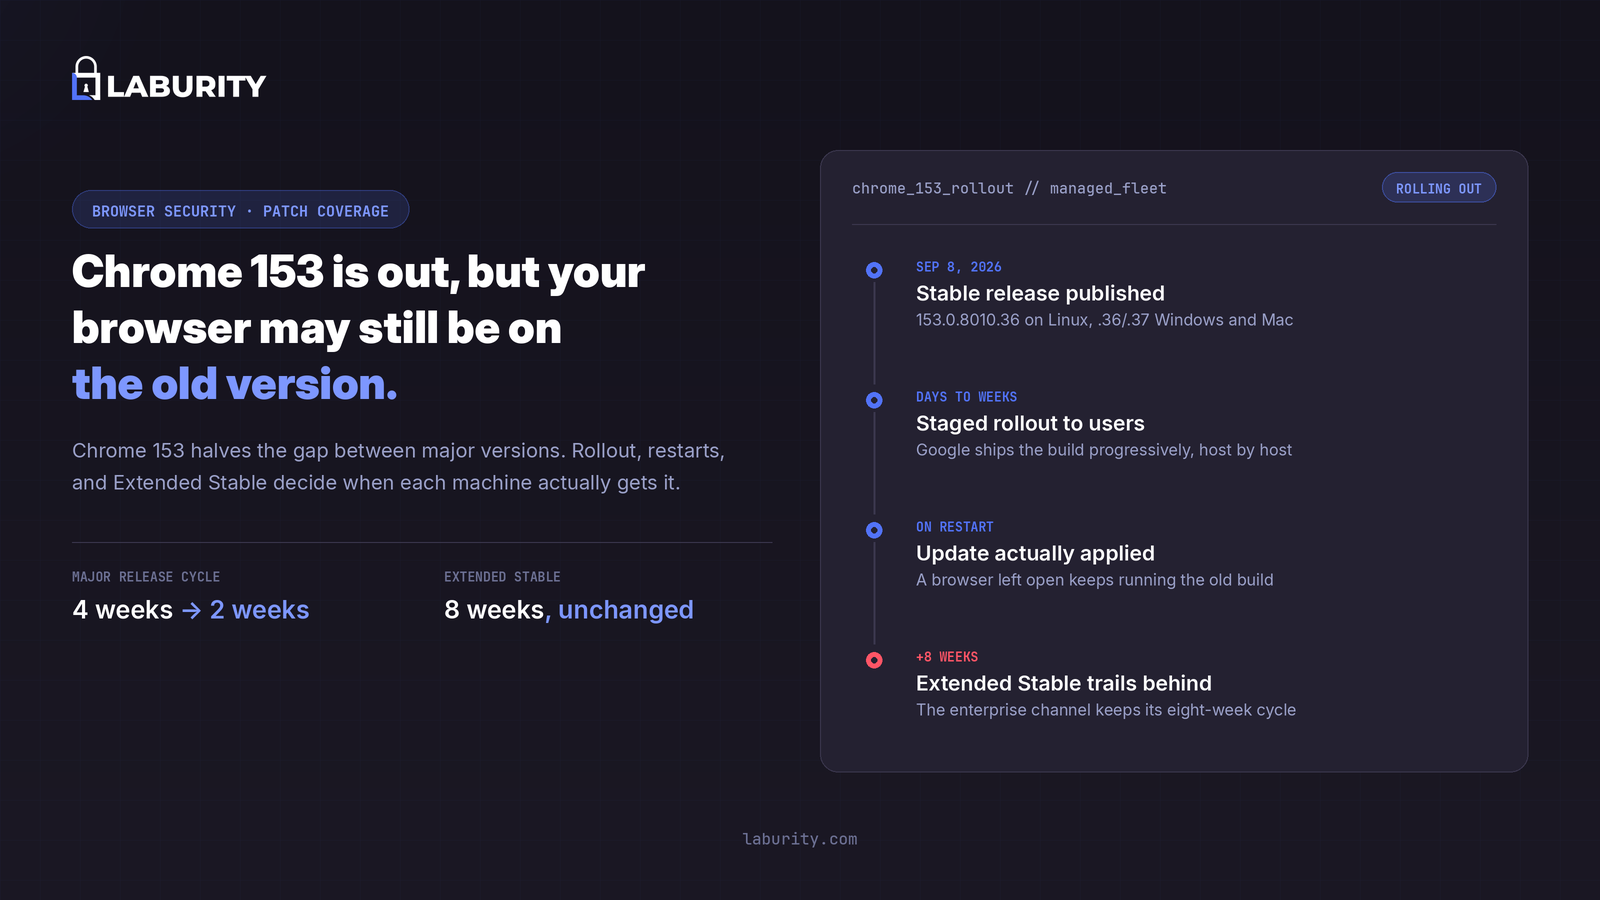
Chrome 153 Is Out but Your Browser May Still Be on the Old Version

Chrome 153, Chrome 153 security update, CVE-2026-87491, Chrome V8 zero-day, Chrome two-week release cycle, Chrome stable channel update, V8 out-of-bounds write, browser patch management, Chrome Extended Stable, Chrome patch gap, browser vulnerability management, Chrome enterprise patching, CVE-2026-85046, CISA Known Exploited Vulnerabilities Chrome, Chrome 153.0.8010.36, endpoint security browser updates, renderer exploitation detection, patch diffing exploits, browser fleet version compliance,

Read article
StyleSmuggler: Magento Zero-Day RCE Exploited in the Wild

StyleSmuggler, CVE-2026-75650, Magento zero-day, Adobe Commerce vulnerability, Magento remote code execution, unauthenticated RCE Magento, Magento template injection, APSB26-146, Magento GraphQL vulnerability, Adobe Commerce hotfix, Magento 2.4.9 security patch, Magento backdoor detection, e-commerce security, Magento incident response, CWE-1336 template engine injection, Magento security patch September 2026, Magento indicators of compromise, web application penetration testing, Magento credent

Read article

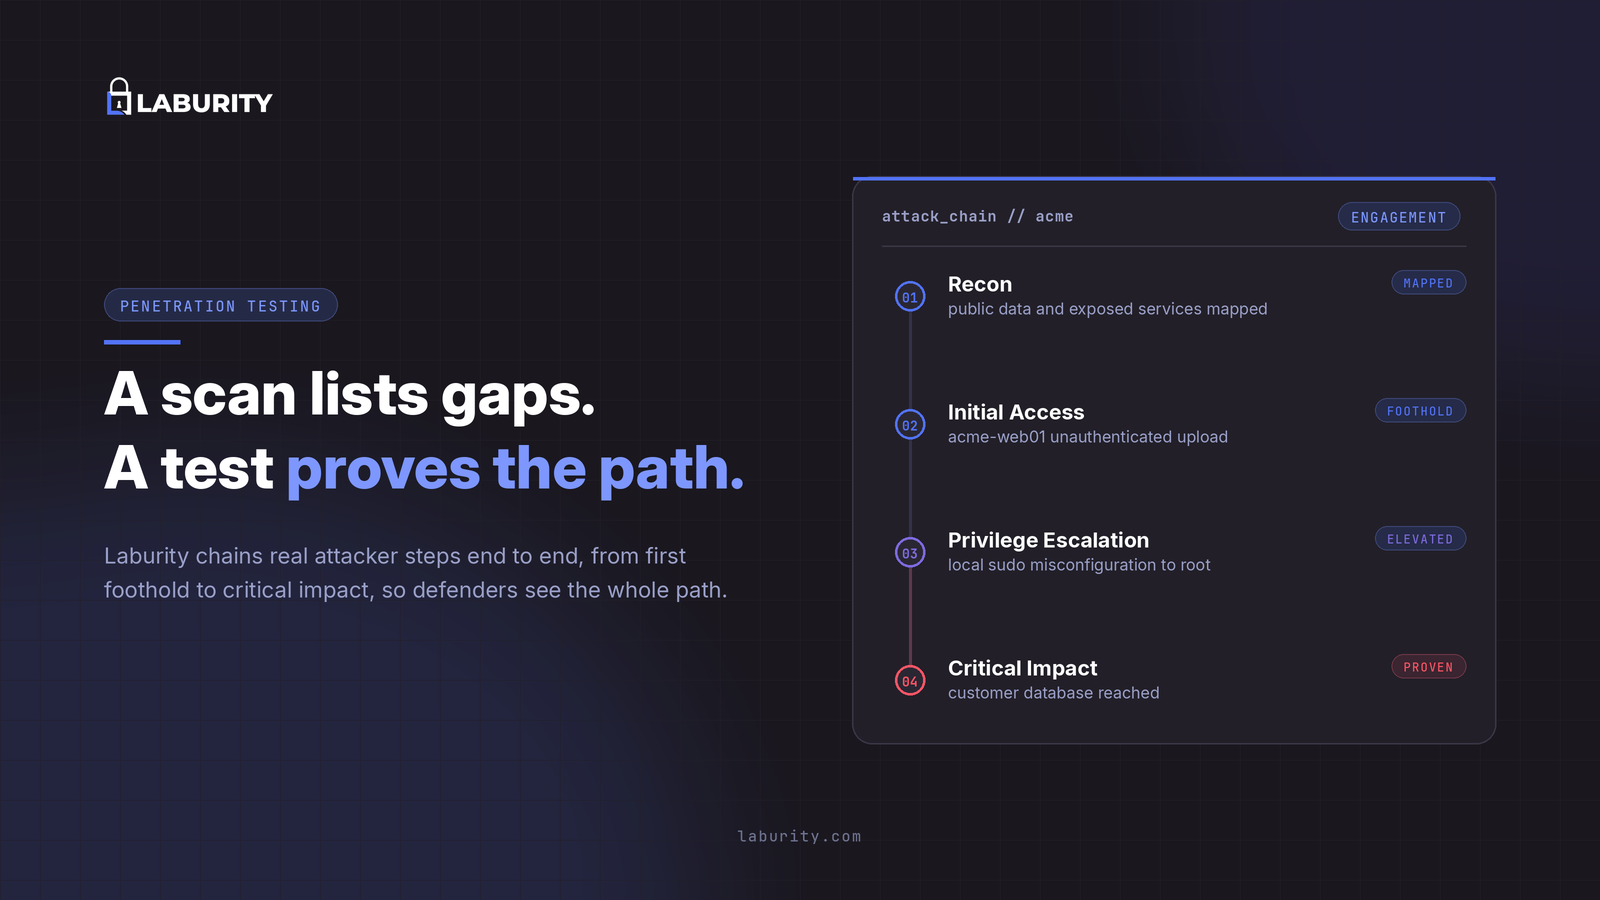
How Penetration Testing Works and Why It Matters

what is penetration testing, penetration testing explained, penetration testing meaning, penetration testing definition, how penetration testing works, penetration testing process, penetration testing methodology, penetration testing steps, penetration testing lifecycle, penetration testing phases, why penetration testing is important, benefits of penetration testing, penetration testing advantages, penetration testing for businesses, penetration testing basics, penetration testing vs vulnerabil

Read article

Fake AI Tools Are Stealing Developer Credentials

A campaign called the OpenClaw Trap uses fake AI tools and cloned GitHub repos to plant infostealers that harvest developer credentials, cloud keys, and tokens.

Read article

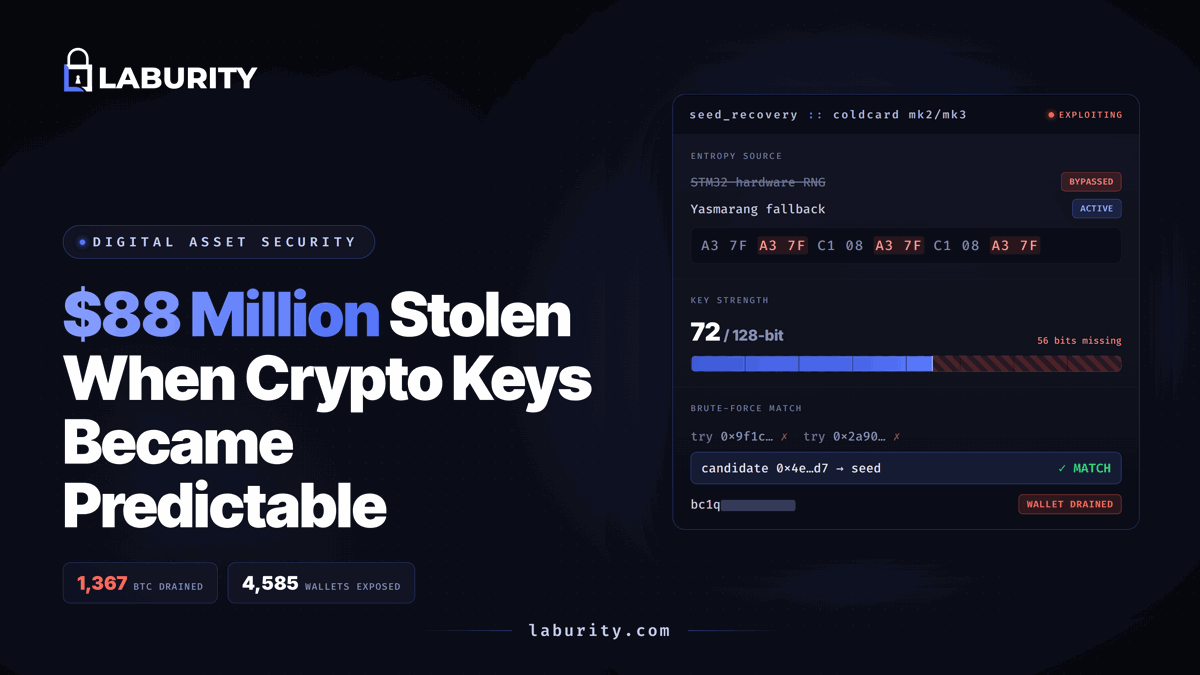
$88 Million Stolen When Crypto Keys Became Predictable

A firmware flaw made Coldcard wallet keys predictable, letting attackers drain ~$88.6M in Bitcoin. What happened, and how to reduce your digital-asset exposure.

Read article

Laburity’s Director Featured in SafetyDetectives Interview

We are excited to share that Hassan Khan Yusufzai, Director at Laburity, was recently featured in an interview with SafetyDetectives .

Read article

Cybersecurity ROI Explained: “Why Investing in Penetration Testing Saves Your Business”

Cybersecurity has to be a major concern for businesses in light of the growing cyber threats and increased regulatory pressure. A single breach can cost a business dearly…

Read article

API Penetration Testing 101: A Beginner’s Guide to Securing APIs

APIs (Application Programming Interfaces) are essential tools that allow different software systems to communicate with each other. A practical example is the Google Maps API…

Read article

Performing Android Static Analysis 101-A Complete Guide for Beginners

Android Static Analysis is a foundational approach to identifying vulnerabilities in applications without executing them. This blog provides insight into the tools and techniques…

Read article

HTTP Request Smuggling Explained: A Beginner’s Guide on identification and mitigation.

There’s a Web application vulnerability called HTTP Request Smuggling that lets attackers sneak harmful requests into a system without detection and by confusing servers about the…

Read article

Penetration Testing Steps: Beginner’s Guide

Penetration testing, also known to many as “pen testing,” is when a simulated cyberattack is conducted against a computer system, network, or web application to assess the…

Read article

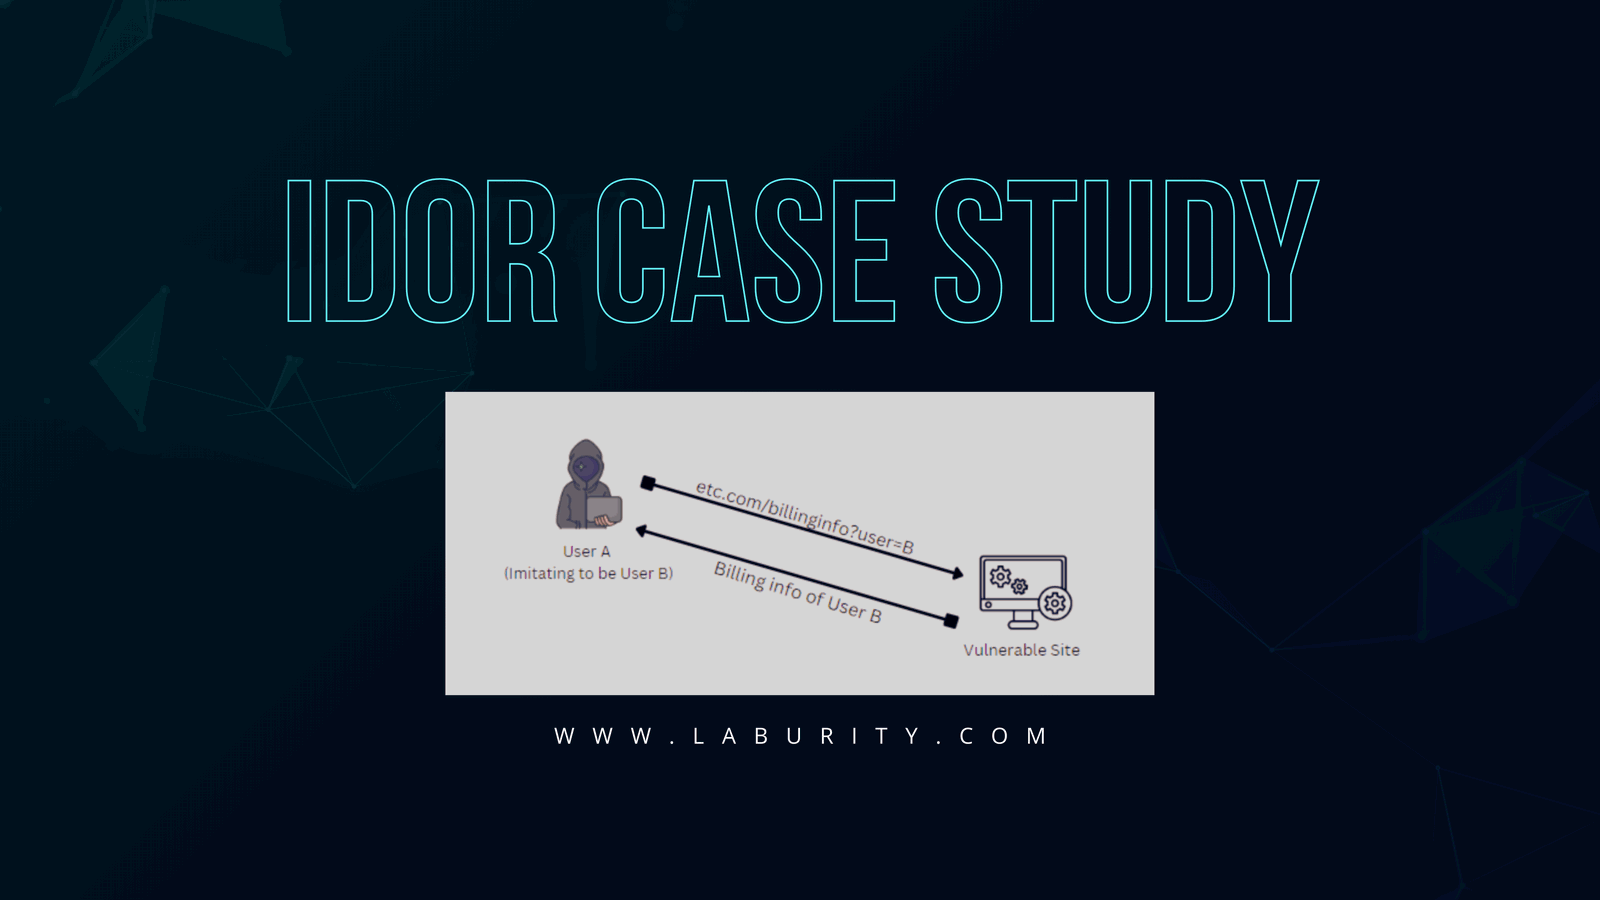
IDOR Case Study: Manipulating Billing Information and Viewing Payment History

We discovered an Insecure Direct Object Reference (IDOR) vulnerability on the redacted website that allowed unauthorized access to billing details and sensitive information. If…

Read article

Exploiting pfsense Remote Code Execution – CVE-2022-31814

Greetings everyone, In this write-up, we will be exploring the interesting exploitation that has been done against the pfsense CVE-2022-31814 .

Read article

Understanding JWT: Basics and Security Risks

JWT, or JSON Web Token, is a fundamental standard outlined in RFC 7519, designed to securely transmit data among parties using JSON objects. Praised for its compactness…

Read article

The Art of Intrusion: File Upload Bypass & WAF XSS Evasion in AWS S3 Demystified

Greetings, today we will be sharing an XSS WAF bypass vulnerability that was identified by one of your Application Penetration Testers while working for a client’s audit. Due to…

Read article

Guardians of the Digital Realm: Unveiling the Importance of a Credible Cyber Security Team

Welcome to the dynamic landscape of the digital era, where the importance of robust cybersecurity has reached unprecedented heights. As businesses increasingly embrace digital…

Read article

Unmasking an RFI to LFI Escalation

Greetings, we are going to share a recent security assessment that was performed for the client, where a seemingly innocent Remote File Inclusion (RFI) unfolded into a more…

Read article

Sneaky Attacks: Critical Account Deletion Vulnerability

In the dynamic landscape of cybersecurity, unearthing vulnerabilities is crucial to fortifying digital platforms. Today, we unravel a significant flaw that allows an attacker to…

Read article

Unveiling Improper Access Control: A Journey into Admin Dashboards

In the ever-evolving landscape of cybersecurity, uncovering vulnerabilities is crucial to maintaining the integrity and security of digital platforms. In this write-up, we explore…

Read article